
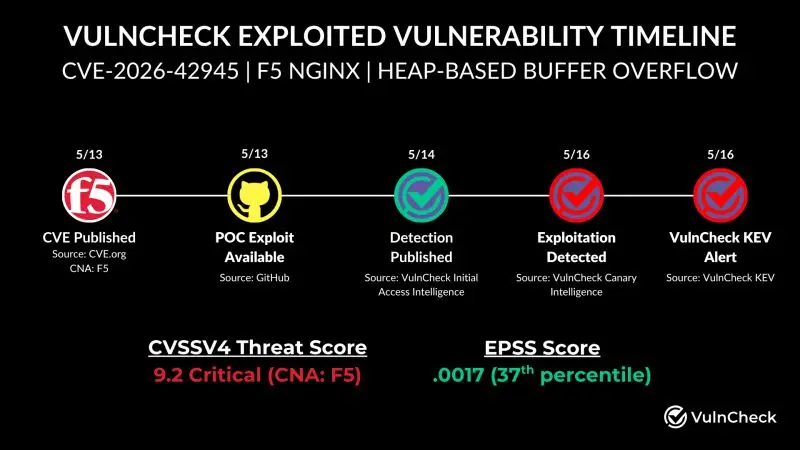
5月13日F5修補網頁伺服器Nginx資安漏洞CVE-2026-42945,此漏洞是在18年前引入,有可能造成伺服器服務中斷(DoS),在特定情況下攻擊者還能用於執行任意程式碼,CVSS v4.0風險為9.2分(滿分10分),如今有研究人員提出警告,他們已偵測到積極利用的現象。
Nginx重大漏洞已被用於攻擊
Posted in
業界新聞
Show the rest Hide the rest
VulnCheck漏洞研究員Patrick Garrity於職場社群網站LinkedIn提出警告,他們在5月16日於蜜罐陷阱首度偵測到CVE-2026-42945被積極利用的跡象。雖然Nginx伺服器必須導入特定的重新寫入組態設定才會受到影響,但由於攻擊者無須通過身分驗證就能利用,再加上全球約有570萬臺伺服器尚未套用新版程式,儘管實際上真正存在風險的伺服器數量有限,VulnCheck也並未說明遭到利用的其他細節,但用戶仍應儘速採取防範措施。
Read the full article on www.ithome.com.tw
#cybersecurity #threatintelligence #riskmanagement #infosecurity | Patrick Garrity 👾🛹💙
We're seeing active exploitation of CVE-2026-42945 in F5 NGINX, a heap buffer overflow affecting both NGINX Plus and NGINX Open Source on VulnCheck Canaries just days after the CVE was published. Yesterday, the VulnCheck Initial Access team noted in our release notes: "An unauthenticated attacker can crash the NGINX worker process by sending crafted HTTP requests. On servers with ASLR disabled — which, of course, is extremely unlikely — code execution is possible. A further caveat is that the target server must be running a specific rewrite configuration to be vulnerable, so not every NGINX instance is exploitable. Our Censys query surfaces roughly 5.7M internet-exposed NGINX servers running a potentially vulnerable version, though the truly exploitable population is likely a much smaller subset." Full release notes are here: https://lnkd.in/eDxGTabZ #cybersecurity #threatintelligence #riskmanagement #infosecurity
www.linkedin.com
Comments (0)
Sign in to comment