Anthropic警告AI會自我複製,並藉IoT散布
新聞Anthropic近日一項研究發現,未來幾個月內,小型AI模型可能就會演化出能在商用物聯網(Internet of Things,IoT)裝置自我複製擴散的能力,形成一種新的AI蠕蟲,且更聰明、更難以封鎖。 過去外界多半擔心強大的AI會劫持昂貴的高階GPU叢集(如資料中心伺服器),為了測試AI模型能否在分散式IoT殭屍網路上執行,Anthropic將研究焦點轉向低成本網路裝置。結果證實,便宜又…
HP EliteBook 6 G1q Powered By Snapdragon X1 Plus Sees Linux Patches
HP EliteBook 6 G1q Powered By Snapdragon X1 Plus Sees Linux Patches Canonical engineer Juerg Haefliger posted a set of Device Tree patches in working to support the mainline Linux kernel on the HP Eli…
Anthropic warns small AI models could self-replicate through IoT devices
Anthropic warns small AI models could self-replicate through IoT devices "Small weight-based replicators" could usher in a new generation of computer worms. https://arstechnica.com/security/2026/10/an…
Python 3.15 goes global with UTF-8 support
After a week’s delay, the new version of Python, v3.15, has been released. With it comes a proper profiler, an experimental just-in-time compiler, and a tightening of dictionary structures. It also of…
US tech giants warn Europe that ditching US tech giants could cost €115B
Some of America's biggest tech companies have a warning for Europe: curb your reliance on US cloud providers, and it could cost you €115 billion. That's the finding of a new study commissioned by CCIA…
Linux Finally Making It Easier To Answer The Question: "Is This RISC-V System…
Linux Finally Making It Easier To Answer The Question: "Is This RISC-V System RVA23?" The RISC-V RVA23 profile is a big deal for reducing fragmentation in the RISC-V ecosystem and standardizing more o…
Welcome to the lovely landlocked land of Luxembork, where the fares are free, and the terminals are techno
There ain't no party like a tap-in party, as nobody ever said. And so it is that one of Luxembourg's mostly redundant tap-in / tap-out terminals is amusing itself by putting on a light show for passin…
BeOS-Inspired Haiku Landed More Hardware Improvements & Other Changes In…
BeOS-Inspired Haiku Landed More Hardware Improvements & Other Changes In September Released at the end of August was Haiku R1 Beta 6 and over the course of September, further improvements continued to…
MITRE ATT&CK第20版登場,新增提示注入、AI輔助資料外洩等攻擊技術
新聞美國非營利組織MITRE在10月13日發布MITRE ATT&CK v20,本次更新的一大重點是新增多項與AI相關的攻擊技術,包括提示注入、AI輔助資料外洩及AI結果污染等,並擴充其他攻擊手法、駭客組織及惡意軟體的相關資料。 在AI相關攻擊技術方面,第20版新增直接提示注入(Direct Prompt Injection,T1699)與間接提示注入(Indirect Prompt Inject…
The Internet’s undersea backbone is slipping into the danger zone
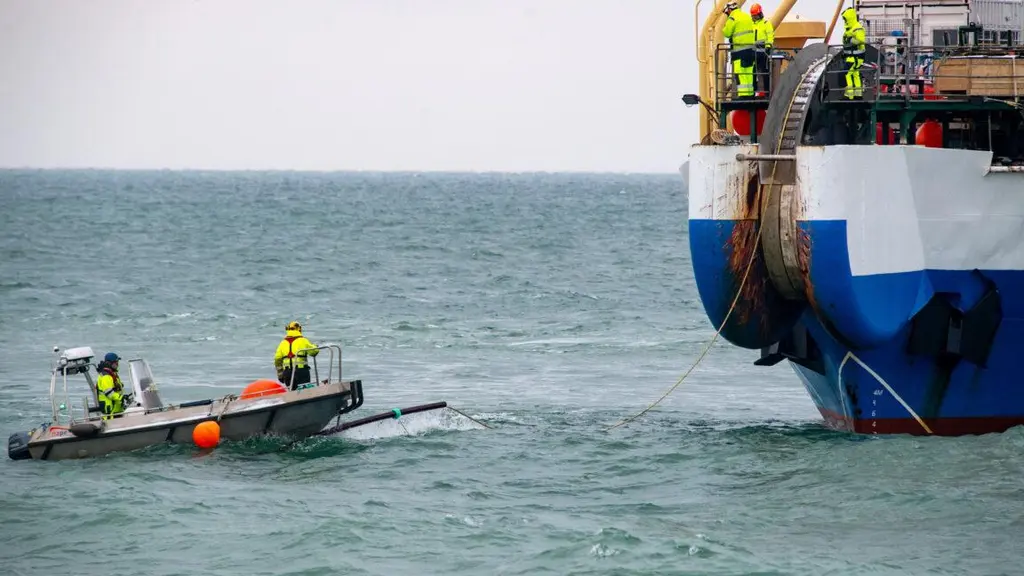
The Internet’s undersea backbone is slipping into the danger zone Elisabeth Braw’s book Undersea War on rising risks for undersea infrastructure. https://arstechnica.com/gadgets/2026/10/the-internets-…
OpenAI, Google pushing new AI models easily tricked into making nudes,…
OpenAI, Google pushing new AI models easily tricked into making nudes, researchers say Attack method exposes flaws in OpenAI, Google safeguards against AI nudes. https://arstechnica.com/tech-policy/20…
OpenAI engineer charged after boardroom bug found wrapped in toilet paper
The Department of Justice has charged an OpenAI engineer with attempting to intercept oral communications after allegedly planting a recording device in an exec conference room. Investigators claim co…
KPMG tech and data boss tells staff facing the boot he's getting promoted
Redundancies might have dented morale at KPMG in the UK, but that didn't stop Paul Henninger, head of technology and data, from sharing some positive personal news with the troops: he's being promoted…
Cloud Hypervisor 54 Released With Live Migration Improvements
Cloud Hypervisor 54 Released With Live Migration Improvements Cloud Hypervisor, the Rust-based Virtual Machine Monitor that began as an Intel open-source project and evolved into a multi-vendor Linux …
Rustls 0.23.46 Released With Four Security Fixes
Rustls 0.23.46 Released With Four Security Fixes Rustls as the modern TLS library written in the Rust programming language with an emphasis on memory safety is out today with its v0.23.46 release in o…
【資安日報】10月14日,微軟發布10月例行更新,修補1,413個資安漏洞
新聞本日新聞焦點 ● 微軟發布10月例行更新,修補1,413個資安漏洞 ● 法國超市冷藏設備遭駭引發歐洲警戒,Copeland設備也列入預警 ● Let's Encrypt明年TLS憑證效期從90天縮至64天,2028年再降至45天 ● Ubuntu開發商Canonical網站遭DDoS攻擊,部分服務中斷 ● OpenAI工程師涉嫌在公司會議室安裝竊聽裝置遭FBI逮捕 資安新聞總覽 Danfoss…
GitLab發布重大安全性更新,修補嚴重程度滿分的資安漏洞
新聞10月12日GitLab開發團隊針對社群版(CE)與企業版(EE)用戶發布資安公告,推出重大修補更新(Critical Patch Release)版本19.4.2、19.3.5,以及19.2.8,總共修補24個弱點,其中重大等級的CVE-2026-97229特別危險,CVSS嚴重程度評分達到滿分10分。由於GitLab曾在一個月前揭露滿分漏洞CVE-2026-85706,公布後不久即出現漏洞…
AI math isn't mathing: infrastructure spending forecast to outstrip expected revenue
AI services are unlikely to deliver enough revenue to cover the expected capital expenditure going into IT infrastructure between now and 2030, and it looks like neocloud operators will largely bow ou…
KDE Plasma 6.8 Released, Marks 30 Years Of The KDE Project
KDE Plasma 6.8 Released, Marks 30 Years Of The KDE Project The feature-packed and polished Plasma 6.8 KDE desktop is now available. Making this release all the more special is that it coincides with t…
Docker Hub修補重大漏洞GhostPat
新聞10月12日Docker發布資安公告指出,他們在9月底接獲研究人員通報,Docker Hub的身分驗證與存取管理機制存在弱點,並在4個小時內重現、確認漏洞,並完成修補。Docker也從該弱點引入Docker Hub的時間點著手清查,確認是否有用戶的帳號轉換曝險,並通知可能受到影響的使用者。此漏洞被登記為CVE-2026-105445,CVSS v4.0嚴重程度評為9.4分,通報此事的研究人員也…
 iThome
Bot
·