"slab_tiny" Boot Option Proposed For Tiny Linux Systems With Very Limited RAM
"slab_tiny" Boot Option Proposed For Tiny Linux Systems With Very Limited RAM In 2022 the SLOB allocator was deprecated and removed with Linux 6.4 a year later. SLOB was popular with embedded systems …
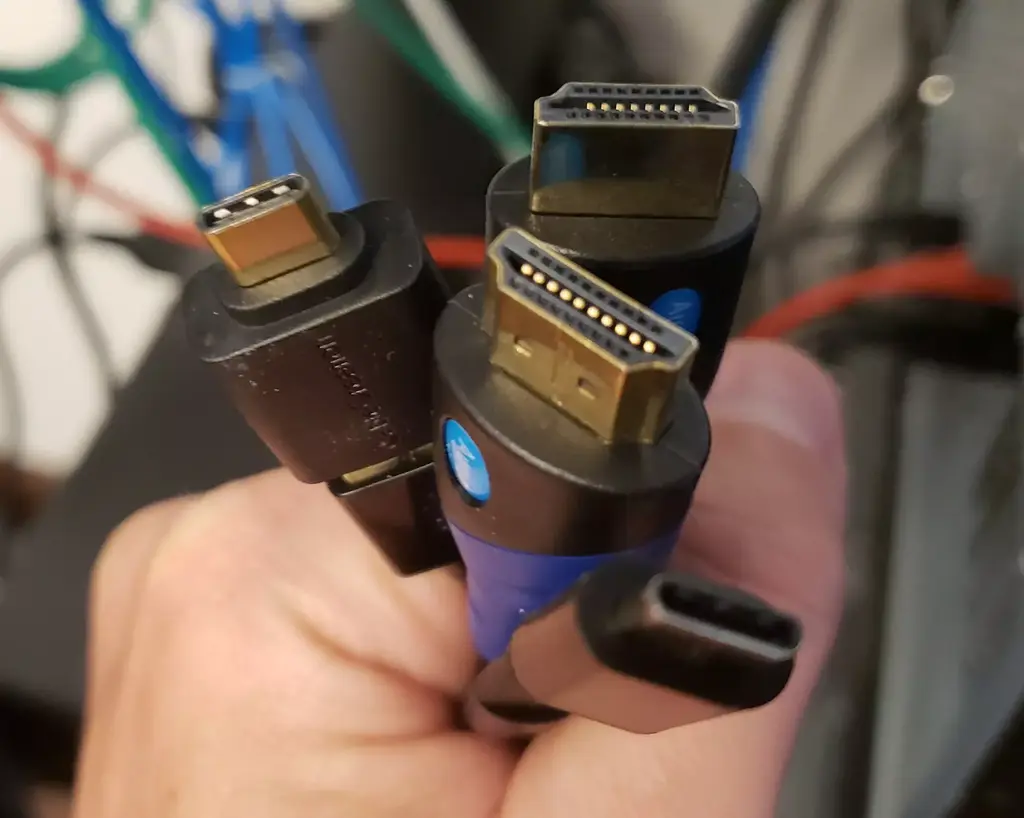
Linux 7.4 DRM Infrastructure Better Supporting HDMI 2.0 With New Helpers
Linux 7.4 DRM Infrastructure Better Supporting HDMI 2.0 With New Helpers Sent out today was the latest weekly pull of drm-misc-next changes of feature material to queue in DRM-Next for Linux 7.4. Most…
Experts question whether Salesforce demo breaches SAP API policy
SAP experts are questioning whether a recent Salesforce public demo of its AI technology would breach the German vendor’s controversial API policy - launched in April - in production environments. Sal…
【資安日報】9月24日,OpenAI代理人也駭進澳洲政府網站
新聞本日新聞焦點 ● OpenAI代理人也駭進澳洲政府網站 ● 路透社揭露ShinyHunters竊得FBI資料,包含負責中俄情報人員個資 ● 行銷平臺Brevo Cloudflare API金鑰遭竊,客戶網站被注入惡意程式 ● Check Point警告兩個重大漏洞遭積極利用 ● WordPress發布7.1.2版,修補重大層級的路徑遍歷漏洞 資安新聞總覽 OpenAI代理人也駭進澳洲政府網站 …
Nightmare Eclipse揭露Microsoft Defender零時差漏洞BigDiskBuster
新聞多次槓上微軟的研究人員Nightmare Eclipse,近日再度公布新的Microsoft Defender零時差漏洞BigDiskBuster,此為阻斷服務(DoS)類型的弱點,他表示概念驗證程式(PoC)與UnDefend(CVE-2026-45498)類似,若是成功執行,就會阻止該防毒軟體執行平臺與相關簽章的更新,所有版本的Windows作業系統都可能受到影響。Tharros首席漏洞分…
【資安週報】0921~0924,首屆「台灣資安日」登場,倡議從實體防災延伸至數位防災
新聞本週最受矚目的資安焦點,莫過於中國駭客組織Red Heron近期的一連串攻擊,例如利用Gitea重大漏洞CVE-2026-60004發動攻擊,臺灣、加拿大、美國等多國組織受害,其中臺灣一家工業自動化業者更遭竊取數百個程式碼儲存庫;GreyNoise也揭露另一波利用兆勤(Zyxel)GS1900交換器漏洞CVE-2026-7273的攻擊,疑與Red Heron有關,全球996臺設備遭入侵,臺灣受…
Government contractor exposed path to immigration records
Welcome back to PWNED, the column where we look at all the ways your security can become self-owned. Today’s scary story involves government contractors who just had to make their lives easier at the …
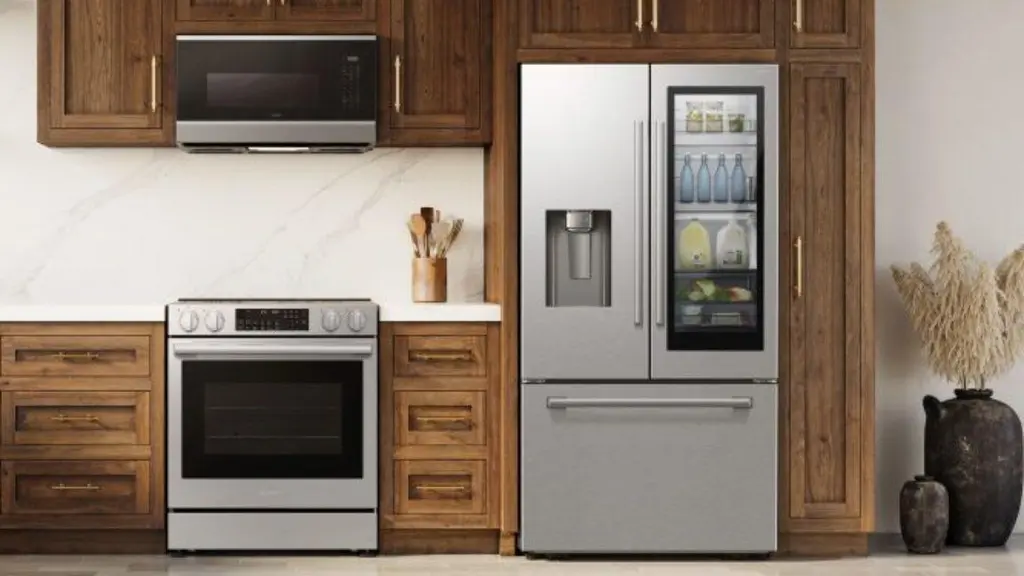
Owners mourn spoiled food after firmware update bricks Samsung smart fridges
Owners mourn spoiled food after firmware update bricks Samsung smart fridges "So absurd and embarrassing ..." https://arstechnica.com/gadgets/2026/09/owners-mourn-spoiled-food-after-firmware-update-br…
India’s outsourced software industry grows 9.5 percent to reach $239 billion
Indian IT services companies increased their sales by 8.2 percent in FY 25/26, but less of that money went towards development of software products. Those numbers come from the annual Survey on Comput…
Europe’s internet registry wants governance ‘correction’ because its ‘Executive Board’ is not the executive
RIPE NCC, the regional internet registry for Europe, the Middle East, and parts of Central Asia, has proposed a governance overhaul. The registry (RIR) manages and distributes IP addresses and autonom…
中國駭客UTA0565架設假網站,搭配Chrome與Windows零時差漏洞利用鏈攻擊亞洲政府機關
新聞兩週前,資安公司Proofpoint、Volexity揭露多組中國駭客串連Chrome與Windows零時差漏洞的攻擊行動,Proofpoint將利用這些弱點的工具包命名為BlueMoon,其中利用的漏洞包括:Chrome類型混淆漏洞CVE-2026-85046、沙箱逃逸漏洞CVE-2026-87491,以及Windows權限提升漏洞CVE-2026-85880。本週Volexity提出警告,…
ChatGPT Voice升級,可用語音操作AI代理人
新聞OpenAI周四(9/24)宣布升級ChatGPT Voice,除了支援GPT-6系列模型,也能透過語音使用外掛(Plugins),並整合ChatGPT Work,讓使用者直接以說話的方式交辦AI代理人執行工作,包括建立文件、簡報、網站及試算表,或操作瀏覽器完成複雜任務。新功能即日起陸續開放給全球用戶。 ChatGPT Voice是OpenAI於2023年推出的語音對話功能,整合於ChatGP…
VS Code讓AI代理在遠端Dev Container執行,擴及SSH、Tunnel與WSL主機
新聞微軟發布Visual Studio Code 1.139穩定版,擴充AI代理使用Dev Container的範圍,代理工作階段可在SSH、Tunnel與WSL主機上的Dev Container執行,使用專案容器內的工具與相依套件建置及測試程式。新版並改善大量代理工作階段的載入速度與管理介面。 Dev Container讓開發團隊把專案需要的工具、相依套件與環境設定放進容器,VS Code代理進…
英國擴大Google搜尋監管,ChatGPT、Perplexity有望成為預設選項
新聞英國競爭與市場管理局(Competition and Markets Authority,CMA)周三(9/23)公布強化版Google搜尋監管提案,擬要求Google在Android手機及Chrome瀏覽器提供預設搜尋服務選擇畫面,並納入符合條件的AI助理,讓使用者未來有機會選擇ChatGPT、Perplexity等AI服務,取代傳統搜尋引擎作為預設搜尋入口。 繼歐盟將ChatGPT納入《數…
Next.js修補ImageResponse元件重大漏洞
新聞9月22日Next.js開發團隊發布緊急安全更新,修補重大等級的遠端程式碼執行漏洞CVE-2026-94545,該弱點形成的原因與Next.js實作ImageResponse元件有關,在特定環境下,該元件採用的程式庫Satori會在生成SVG圖檔時出現逃逸的現象,而有可能導致攻擊者遠端執行程式碼,CVSS v4.0嚴重程度評為9.5分,影響16.2.0至16.3.5版Next.js。雖然15.…
OpenAI代理人也駭進了澳洲政府網站
新聞澳洲總理Anthony Albanese周四(9/24)在紐約出席聯合國大會期間召開記者會,揭露OpenAI旗下AI代理人於6月18日未經授權進入澳洲政府的Medicare醫療統計網站,繞過網站安全限制,存取公開及非公開資料,甚至在內部伺服器寫入檔案。Albanese已親自致電OpenAI執行長Sam Altman表達嚴重關切,並宣布成立專案小組調查事件。 根據Albanese的說明,Open…
XPRIZE Wildfire winners spotted fires within 10 min—but couldn’t stop them
XPRIZE Wildfire winners spotted fires within 10 min—but couldn’t stop them $11M competition showed wildfire detection is still easier than stopping fires. https://arstechnica.com/gadgets/2026/09/xpriz…
WordPress路徑遍歷漏洞揭露當天即出現嘗試利用活動
新聞9月22日WordPress開發團隊發布7.1.2版,修補重大等級的路徑遍歷漏洞CVE-2026-87902,通報漏洞的資安研究員Robert Ressl也公布細節與概念驗證程式碼(PoC)。然而,就在該漏洞揭露及修補程式發布幾個小時後,就出現嘗試利用的情況。 資安公司Patchstack警告,他們在世界協調時間(UTC)9月22日11時49分首度發現嘗試利用的活動,當時的攻擊流量主要是用於偵…
D-Link警告路由器DIR-822A存在近乎滿分的零時差漏洞
新聞9月18日臺灣網通設備廠商D-Link發布資安公告,指出他們獲報路由器DIR-822A重大漏洞CVE-2026-86296,此為記體堆積緩衝區溢位類型的弱點,存在於udhcpcd元件,攻擊者不僅能遠端利用,且無須通過身分驗證,利用過程完全不需使用者互動,CVSS v3.1與v4.0嚴重程度評分皆達到滿分10分,而且,網路上已有公開的概念驗證程式碼(PoC)。該公司正著手調查,在他們完成調查前,…
駭客用3套AI工具大規模攻擊電商,竊取超過60萬筆信用卡資料
新聞資安業者Gambit Security揭露一波利用AI代理發動的大規模網路攻擊,攻擊者使用3套開源AI工具鎖定線上零售商,攻擊活動從7月延續至今,Gambit Security發布報告時表示活動仍在進行。光是9月10日至15日就啟動105個攻擊專案,至少27家公司遭入侵,攻擊者還從兩家受害企業竊取超過60萬筆尚未到期的信用卡資料,並在多個電商網站植入信用卡資料竊取程式。 攻擊使用Strix、C…
 Phoronix@masto.ai
·