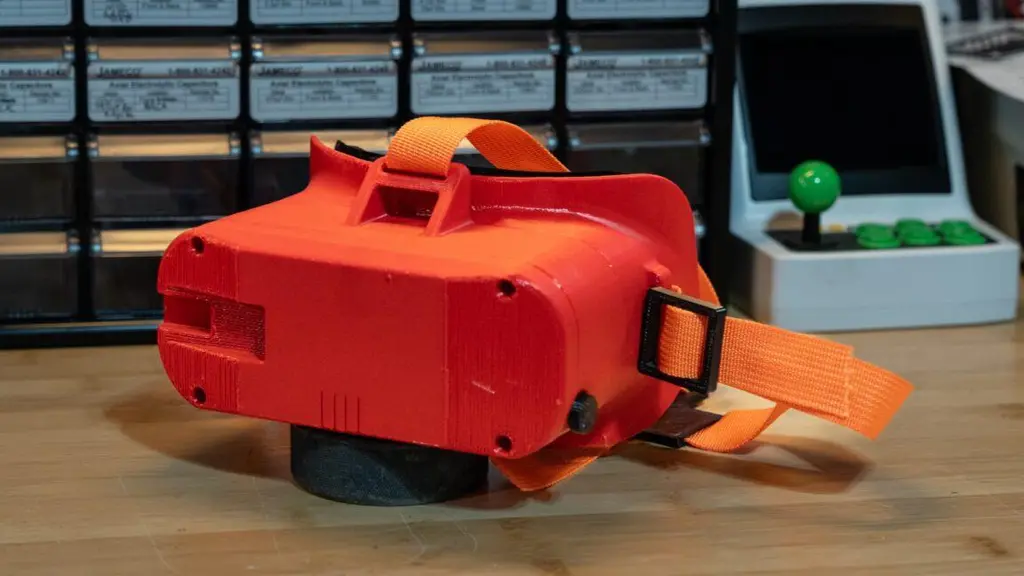
DIY VR: How to build your own headset, and why you probably won't want to
DIY VR: How to build your own headset, and why you probably won't want to A primer on the joys and pains of building your own head-mounted display. https://arstechnica.com/gadgets/2026/10/diy-vr-how-t…
Cloudflare建立爬蟲信任評等,預計供網站控管流量
新聞Cloudflare公布爬蟲信任評估機制,針對已通過身分驗證的機器人,持續觀察是否遵守網站抓取規則,以及收到降低請求頻率的要求後是否配合,再依長期行為建立信任評等。該機制目前已在內部使用,未來預計開放客戶設定信任門檻,決定如何處理爬蟲流量。 評估對象是Cloudflare的已驗證機器人(Verified Bots),原有機制會確認爬蟲身分及宣稱的用途,並要求不得濫用網站資源。不過,機器人即使通…
GNOME Mutter Lands Improvement For Reducing GPU Work While In Power Savings Mode
GNOME Mutter Lands Improvement For Reducing GPU Work While In Power Savings Mode Stemming from a bug report one month ago with GNOME 51 over high GPU usage while the monitor is sleeping, a set of 17 p…
Dr Garry Hunt talks to us about the astonishing Voyager probes
It's been nearly half a century since the Voyager probes launched from Earth on a mission to explore the outer solar system, and they're still running. You can listen to the latest episode of The Kett…
Broadcom Wi-Fi bug turns sweet 16, still lets strangers hijack your router
A 16-year-old security flaw in Broadcom's Wi-Fi software could let attackers hijack millions of routers without knowing the network password, even though the chipmaker reportedly knew about the proble…
SpacemiT Announces The V100 Server-Class RISC-V Processor
SpacemiT Announces The V100 Server-Class RISC-V Processor Following the interesting SpacemiT K3 RVA23 RISC-V SoC, SpacemiT today announced the V100 server-class RISC-V processor... https://www.phoroni…
Linux核心PwnEscape漏洞可突破虛擬機隔離,導致主機記憶體洩漏
新聞資安研究團隊pwn.ai揭露Linux核心重大漏洞PwnEscape(CVE-2026-99999)。在使用受影響Linux核心的虛擬化環境中,攻擊者可能透過虛擬機器送出特製網路封包,讀取底層主機記憶體,Vercel也證實,研究人員已在Sandbox正式環境成功取得底層主機的記憶體資料。Linux核心已發布修補程式,該漏洞風險評分為9.3分,屬重大等級。 研究人員Paulos Yibelo今年…
Vercel Labs推出tsc-ts,以TypeScript重寫Go版TypeScript 7編譯器
新聞Vercel旗下開發團隊Vercel Labs推出開放原始碼編譯器tsc-ts,將微軟以Go語言開發的TypeScript 7.0.2編譯器重新以TypeScript實作,再透過自家工具scriptc轉換成可直接執行的原生程式。新工具支援型別檢查、JavaScript程式碼輸出及增量建置,目前仍屬實驗性專案。 TypeScript是JavaScript的延伸語言,可在開發階段檢查程式碼中的資料…
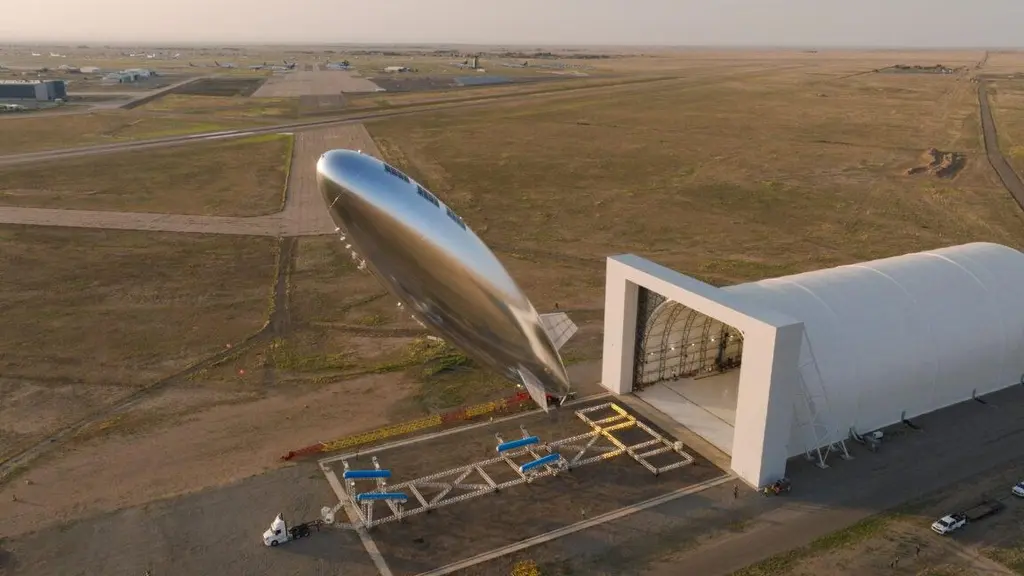
Trans-Pacific journey tested stratospheric cell tower concept in Japan
Trans-Pacific journey tested stratospheric cell tower concept in Japan Tests showed Sceye’s high-flying platform can deliver connectivity in disasters. https://arstechnica.com/gadgets/2026/10/trans-pa…
Museum exhibit reveals the intricate workings of a knackered Dell
Today's entry in the catalog of bork comes from Coventry's Herbert Art Gallery & Museum, where an information terminal is showing more about the hardware behind the scenes than the objects on display.…
BeamFS Sent Out As Newest File-System Proposal For Linux
BeamFS Sent Out As Newest File-System Proposal For Linux There is yet-another-Linux-file-system attempt... An initial request for comments (RFC) patch series was sent out this morning for BeamFS. The …
【資安日報】10月19日,Google揭露中國相關駭客利用BeyondTrust零時差漏洞入侵企業內網
新聞本日新聞焦點 ● Google揭露中國相關駭客利用BeyondTrust零時差漏洞入侵企業內網 ● 中國駭客UAT-11985濫用Google服務從事網釣,鎖定臺灣研究機構 ● 駭客組織UNC5820鎖定電信公司,利用Fortinet漏洞散布惡意軟體 ● OpenBSD修補存在37年的漏洞,研究人員已公開攻擊程式 ● 162個M365租戶遭未授權存取,ConnectWise備份API憑證遭濫用…
Arch Linux軟體市集出現惡意套件,攻擊者藉此散布惡意程式以取得root權限
新聞Arch Linux社群套件庫AUR(Arch User Repository)再傳惡意套件攻擊,根據資安新聞網站Bleeping Computer的報導,攻擊者以拼字相近的名稱偽冒熱門AUR輔助工具yay與paru,將包含惡意安裝腳本的套件上傳至AUR。使用者若誤將其安裝到系統中,可能導致攻擊者執行具root權限的遠端Shell指令,進而取得系統的高權限控制能力。 這波攻擊於10月13日發現…
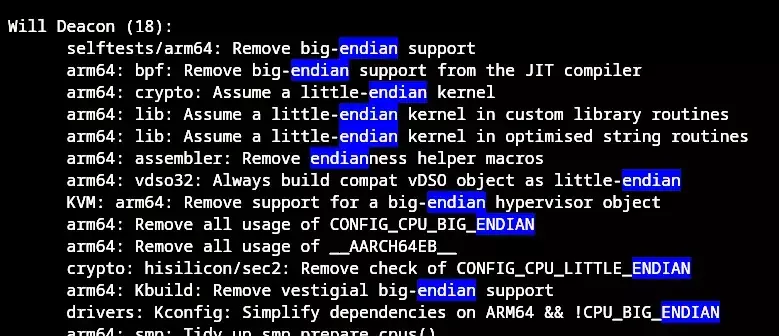
Linux 7.4 Removing Its Broken & Rarely Touched Code For ARM64 Big Endian
Linux 7.4 Removing Its Broken & Rarely Touched Code For ARM64 Big Endian The ARM64 code for Linux 7.4 is stripping away its support for big-endian kernel builds for 64-bit ARM... https://www.phoronix.…
RADV Promotes VK_EXT_host_image_copy To Enabled By Default For RDNA1 GPUs
RADV Promotes VK_EXT_host_image_copy To Enabled By Default For RDNA1 GPUs Going back to July 2025 the open-source Radeon RADV Vulkan driver has offered experimental host image copy support with the AP…
Microsoft’s second-hand licensing appeal gets the brush-off
Microsoft has failed to win permission to appeal to the UK Supreme Court in the long-running legal spat with ValueLicensing after the Court of Appeal refused its application. The US megacorp was chall…
TAINT_FORCED_BIND Sent In For Linux 7.4 To Deal With Major Fuzzing Attack
TAINT_FORCED_BIND Sent In For Linux 7.4 To Deal With Major Fuzzing Attack Among the early pull requests sent out in advance of the Linux 7.4 kernel merge window opening were the driver core updates. S…
Drupal修補重大RCE漏洞,呼籲用戶儘速採取行動
新聞10月14日內容管理系統Drupal開發團隊發布資安公告,修補兩個重大等級的資安漏洞CVE-2026-108097、CVE-2026-108099,攻擊者都有機會將其用於遠端執行任意程式碼(RCE),在Drupal的嚴重程度評分裡,皆被評為19分(滿分25分),呼籲用戶應儘速套用新版程式修補。 其中CVE-2026-108097存在於Drupal Core,影響Field UI模組,開發團隊強…
雲端版辦公室軟體Collabora Online漏洞遭到利用,攻擊者試圖入侵Nextcloud伺服器
新聞10月14日美國國家漏洞資料庫(NVD)揭露重大等級的漏洞CVE-2026-110447,此弱點存在於雲端服務Nextcloud的應用程式Collabora Online Built-in CODE Server(richdocumentscode),可被用於遠端程式碼執行(RCE),CVSS v4.0嚴重程度評分為9.2,此為作業系統命令注入漏洞,存在於proxy.php元件,在CODE S…
AI inference is running into a memory bottleneck. Huawei wants to tackle it with OceanStor M900
As organizations move from straightforward AI interactions towards longer conversations, complex reasoning and autonomous agents, the demands on their infrastructure are changing. Processing increasin…