Grok chat duped into swallowing injected instructions
xAI's Grok web chat agent is currently vulnerable to a novel form of prompt injection, according to security researchers with Adversa AI. The technique allows an attacker to create a web page poisoned…
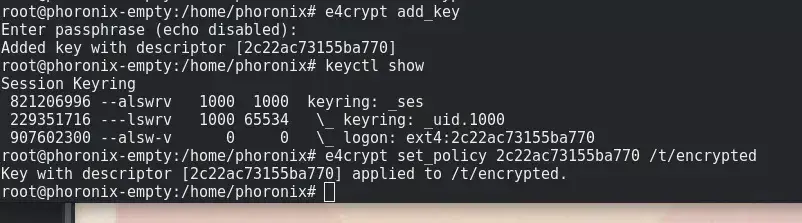
FSCRYPT Sees Cleanup With Linux 7.3 To Open Door For More Features Like Btrfs…
FSCRYPT Sees Cleanup With Linux 7.3 To Open Door For More Features Like Btrfs Encryption FSCRYPT is the Linux file-system encryption framework for supporting per-directory, transparent encryption. FSC…
Grok exfiltrates user data when malicious instructions are encrypted
Grok exfiltrates user data when malicious instructions are encrypted Cryptographic Context Injection is only the latest way to break an LLM safety guardrail. https://arstechnica.com/security/2026/08/g…
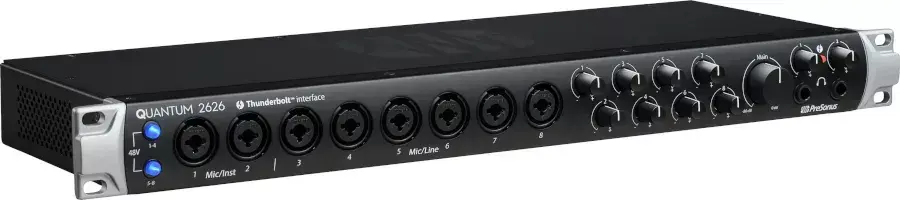
Linux Driver Posted For The PreSonus Quantum 2626: A ~$700 Thunderbolt Audio…
Linux Driver Posted For The PreSonus Quantum 2626: A ~$700 Thunderbolt Audio Interface The PreSonus Quantum 2626 is a high-end, Thunderbolt 3 based audio interface. PreSonus just maintains Windows and…
OpenAI glitch locks out vetted cyber researchers – and some can't get back in
OpenAI says a technical stuff-up booted some vetted security researchers out of its Trusted Access for Cyber (TAC) program, only for its recovery process to decide some of them aren't welcome back. Th…
French tax authority says break-in exposed data of 600K, including some private messages
France's tax authority says attackers may have stolen the contents of messages exchanged with hundreds of taxpayers during the data raid it confirmed last week. In an update published this week, the G…
RPM 6.1 Released With Clang Build Fixes, New Release Model
RPM 6.1 Released With Clang Build Fixes, New Release Model RPM 6.1 is out today as the newest feature release for this package management system. With RPM 6.1 comes a number of features and improvemen…
Akamai揭露自帶EDR攻擊手法,利用EDR當武器執行惡意程式碼
新聞為了繞過EDR與防毒軟體等端點防護機制,時下駭客最常用的攻擊手法,莫過於自帶驅動程式(Bring Your Own Vulnerable Driver,BYOVD),藉由存在弱點的核心驅動程式,干擾EDR等防護機制運作,不過最近有資安公司揭露新的攻擊手法,直接將EDR系統變成攻擊工具。 資安公司Akamai於資安大會DEF CON 2026(DEF CON 34)上,公布一種叫做自帶EDR(B…
Microsoft probes reports of games taking exception to Windows 11's August update
Microsoft is investigating reports of games crashing after users installed August's Patch Tuesday update for Windows 11. The company acknowledged the reports on its Release Health page. Affected games…
New Study Challenges Common Assumptions About Screen Time For Kids…
New Study Challenges Common Assumptions About Screen Time For Kids https://hardware.slashdot.org/story/26/08/19/2231240/new-study-challenges-common-assumptions-about-screen-time-for-kids?utm_source=rs…
Mesa 26.2.1 Released With Dozens Of Fixes
Mesa 26.2.1 Released With Dozens Of Fixes For those preferring the tradition of waiting for the first point release of a new Mesa feature release before upgrading, Mesa 26.2.1 is available today with …
Linux 7.3 Cleans Up The Code For Disabling Of Legacy 32-bit Time Support
Linux 7.3 Cleans Up The Code For Disabling Of Legacy 32-bit Time Support The Linux kernel has supported the CONFIG_COMPAT_32BIT_TIME Kconfig build time option for optionally disabling of legacy 32-bit…
No lift for Swift as NASA abandons orbital rescue
NASA and Katalyst Space have abandoned an ambitious attempt to boost the Swift observatory into a higher orbit and postpone its fiery return to Earth. Katalyst Space's LINK spacecraft will still attem…
Software development and tech services in the cross-hairs as AI marches on
Business transformation, software development, and technology implementation are among the tech job categories likely to be hit hardest by AI, according to new research from Forrester. The global IT a…
KDE Gear 26.08 Delivers The Latest KDE App Experience
KDE Gear 26.08 Delivers The Latest KDE App Experience KDE Gear 26.08 was released today to deliver the latest collection of KDE application updates... https://www.phoronix.com/news/KDE-Gear-26.08
MacSync竊資軟體輪替C2增加網域封鎖難度,竊取鑰匙圈與雲端憑證後分段送出
新聞微軟資安研究團隊揭露竊資軟體MacSync Stealer最新攻擊活動,從端點與網路活動追查出30多個相關網域。MacSync會持續更換用於下載惡意酬載、命令與控制(C2)通訊及資料傳送的網域與其他攻擊基礎設施,使單靠封鎖惡意網域及比對既有入侵指標的防禦方式效果降低。企業還需搭配終端機操作、憑證存取及資料傳送等行為,辨識可能的異常活動。 MacSync專門鎖定macOS裝置,研究團隊觀察到的攻…
SparkyLinux 8.4 rekindles support for 32-bit PCs
Almost exactly a year after SparkyLinux 8.0 abandoned installation images for 32-bit PCs, version 8.4 has brought them back. The distro remains based on Debian 13 and retains the codename "the Seven S…
Google擴大與Marvell AI晶片合作,採購規模上看1,200億美元
新聞根據晶片設計公司Marvell Technology周三(8/19)提交給美國證券交易委員會(SEC)的文件,該公司已與Google在7月底簽署商業協議,擴大合作開發客製化AI晶片,Google未來採購規模上看1,200億美元。 今年4月市場就傳出Marvell與Google在打算共同開發可用來搭配Google現有TPU(張量處理器)的晶片,根據Marvell在文件中的解釋,這次協議所涵蓋的客…
Vercel開源輕量程式設計代理fx,可直接執行也能嵌入開發工具
新聞建立並主導Next.js開發的Vercel,近年持續投入AI開發工具,現在開源程式設計代理fx。fx原本是Vercel內部工具,以程式語言Zig語言開發,採Apache-2.0授權,設計重點是縮小執行規模並降低啟動與資源負擔。開發者除了能直接把fx當成命令列工具使用,也能將代理功能整合進編輯器、網站或其他開發系統。目前fx仍屬實驗性專案。 fx的主要用途,是替AI模型提供執行程式開發工作的環境…
資安署揭機關網站驗證機制失效資安事件,密碼重設與OTP驗證遭繞過
新聞數位發展部資通安全署(資安署)資通安全網路月報每期內容當中,都會回顧政府機關網站最近遭遇的資安重大事件案例,而在本週發布的115年7月月報檢討的狀況,是近期發現的機關網站密碼重設與一次性密碼(OTP)驗證機制失效事件,結果導致攻擊者得以繞過雙重驗證、修改密碼,甚至有管理帳號因此被非法登入的情形。 資安署特別以兩個案例來說明:首先,是驗證碼以明碼形式外洩的問題,導致攻擊者無須收取驗證碼郵件,即能…
 The Register
Bot
·