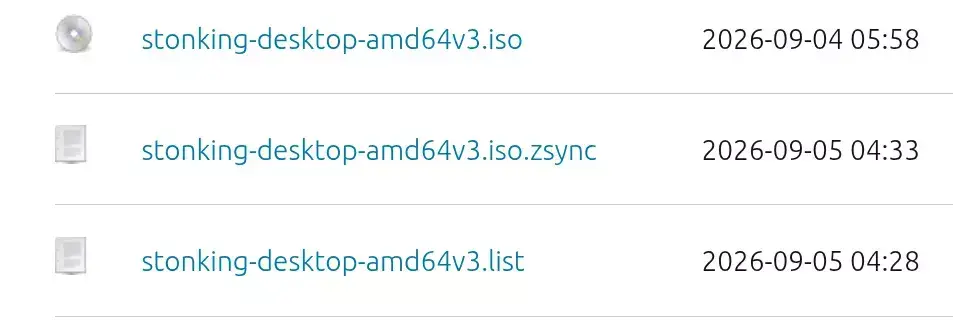
Ubuntu 26.10 amd64v3 Daily ISOs Now Being Published
Ubuntu 26.10 amd64v3 Daily ISOs Now Being Published As an interesting development for Ubuntu 26.10, the daily ISOs of the "Stonking Stingray" now include amd64v3 images... https://www.phoronix.com/new…
Nitter lives to proxy another day after taking legal advice
The Nitter project will continue "following legal advice," meaning XCancel, a public service built on its open source code, is back online. As of September 7, nitter.net displayed the announcement: "F…
Welsh environment regulator's FoI blunder exposes diversity data of 2,000 staff
Natural Resources Wales (NRW) says diversity data belonging to around 2,000 current and former employees who worked at the environmental regulator between April 2013 and March 2018 was exposed in a cl…
Smartphone makers don't bother to comply with EU repairability requirements
One year into the EU's repairability rules for smartphones and tablets, more than 80 percent of devices still lack the necessary repair information, Right to Repair Europe reports. The campaign group …
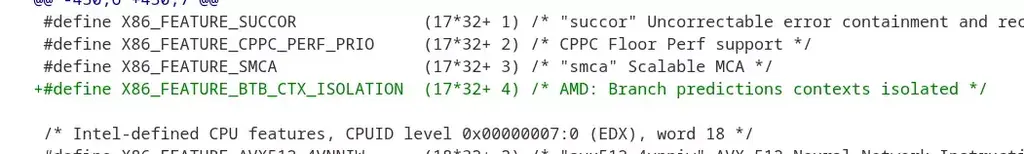
Linux Preps For New AMD Zen 6 BTB CTX Isolation Security Feature
Linux Preps For New AMD Zen 6 BTB CTX Isolation Security Feature A recently posted Linux kernel patch has revealed a new security improvement with Zen 6 processors... https://www.phoronix.com/news/Lin…
'The Jobs Apocalypse Is Postponed. An AI Jobs Boom Is Here'…
'The Jobs Apocalypse Is Postponed. An AI Jobs Boom Is Here' https://slashdot.org/story/26/09/06/214258/the-jobs-apocalypse-is-postponed-an-ai-jobs-boom-is-here?utm_source=rss1.0mainlinkanon
UK food supply chain at risk from hostile attacks
A UK watchdog is warning that cyber criminals making moves against online systems in the food supply chain could cause serious upset, following damaging attacks on the Co-op and Marks & Spencer last y…
疑似北韓駭客將後門植入負載平衡器HAProxy,可攔截流量並讓C2請求避開後端日誌
新聞資安業者Rapid7揭露一套鎖定南韓媒體與汽車業的Linux攻擊工具,其中Ted後門被直接植入HAProxy負載平衡器,可在正常處理網站流量的同時攔截HTTP連線、竊取登入工作階段Cookie、執行遠端命令,還能修改特定使用者收到的網頁內容。Rapid7研判,攻擊者與北韓進階持續性威脅(APT)組織有關,相關活動可能從2025年初就已展開。 攻擊者使用HAProxy 2.8.12重新編譯出惡意…
因應歐盟DPP,臺灣試行推動產品數位護照,開源DPP模組助企業接軌歐盟
新聞面對歐盟逐步推動產品數位護照(Digital Product Passport, DPP)制度,國內正加速建立產品生命週期資訊管理能力。環境部今天(9/7)與國內產業展示我國推動DPP4年試行成果,期望通過政府與產業合作,建立產品資訊蒐集、交換及應用模式。 循環署署長賴瑩瑩指出,產品數位護照的核心並不是單純的揭露產品資訊,而是透過產品全生命週期資料,掌握產品從製造、使用、維修到回收再利用的完整…
西雅圖時報與Newsday控告OpenAI、微軟,要求銷毀納入其新聞內容的AI模型
新聞美國媒體西雅圖時報與Newsday向紐約南區聯邦地方法院,控告OpenAI與微軟侵犯著作權,指控兩家公司未經授權使用新聞內容訓練AI,並在搜尋與生成回答時取用西雅圖時報與Newsday的報導。兩家媒體要求損害賠償、禁止被指控的侵權行為,並要求法院扣押或銷毀納入西雅圖時報與Newsday新聞內容或衍生內容的大型語言模型與訓練資料集。 西雅圖時報與Newsday主張,OpenAI與微軟取得新聞內容…
PostgreSQL邏輯解碼漏洞藏12年,複寫帳號可載入任意程式碼
新聞資安業者Cyera公開PostgreSQL漏洞CVE-2026-6471的技術細節,問題可追溯至2014年PostgreSQL 9.4加入的邏輯解碼功能。在已啟用邏輯解碼的PostgreSQL伺服器上,持有REPLICATION複寫權限,但非超級使用者的帳號,可要求PostgreSQL載入指定的程式碼函式庫,以資料庫服務使用的作業系統帳號執行任意程式碼。 邏輯解碼會把PostgreSQL記錄的…
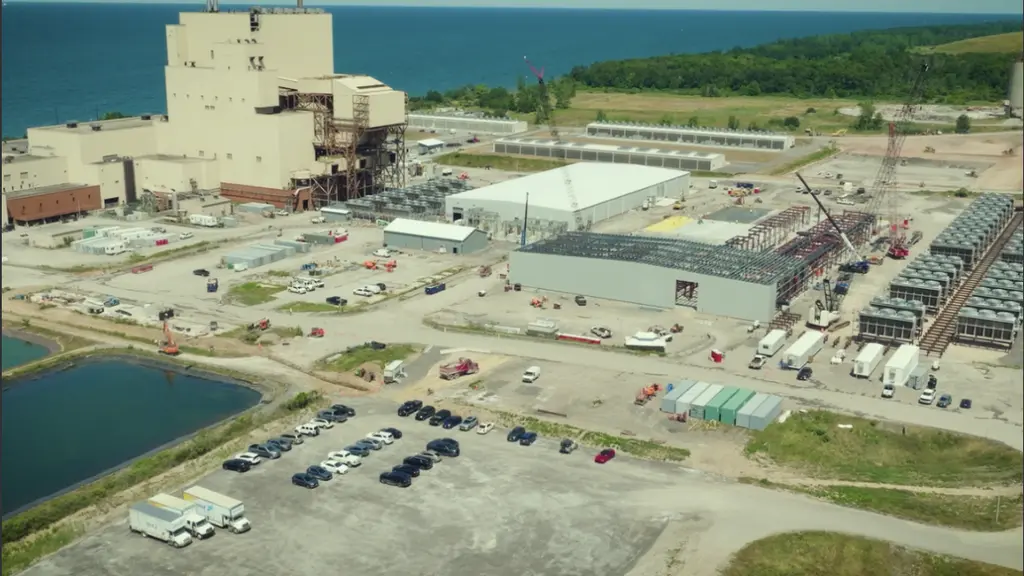
The AI data center boom is causing new accountability problems
The AI data center boom is causing new accountability problems When multiple companies are behind one project, who bears responsibility for problems? https://arstechnica.com/ai/2026/09/the-ai-data-cen…
Nouveau Preparations For HDMI 2.1 DSC, AMD HDMI FreeSync Fixes For Linux 7.4
Nouveau Preparations For HDMI 2.1 DSC, AMD HDMI FreeSync Fixes For Linux 7.4 Last week's set of DRM-Misc-Next changes submitted to DRM-Next with targeting the upcoming Linux 7.4 kernel cycle features …
Intel's Dynamic PAMT Appears Ready For Linux 7.4 To Help With TDX Memory…
Intel's Dynamic PAMT Appears Ready For Linux 7.4 To Help With TDX Memory Overhead Intel's Dynamic PAMT feature looks like it's finally going to be ready for mainline with Linux 7.4. The Intel Dynamic …
Rustls 0.23.44 Released With ML-DSA Certificates Enabled By Default
Rustls 0.23.44 Released With ML-DSA Certificates Enabled By Default Rustls as the modern TLS library implementation written in the Rust programming language is out with a new feature release. This mor…
【資安日報】9月7日,SEMI E187驗證標章亮相,最快10月公布首家驗證機構,第一波獲得認可的產品年底有望問世
新聞本日新聞焦點 ● SEMI E187驗證標章亮相,首波通過認證產品年底前問世 ● 中科院傳出採購網大量派送過期資訊,起因是遭遇外部攻擊 ● OpenAI代理人連上德文論壇共商解題,且1個多月才被發現 ● 電商平臺Magento、Adobe Commerce遭零時差漏洞攻擊 ● AWS高權限Root使用者遭密碼噴灑,逾150個組織成攻擊目標 資安新聞總覽 中科院傳出採購網大量派送過期資訊,起因是…
PaperCut零時差漏洞攻擊鎖定歐美學校
新聞8月底列印管理軟體廠商PaperCut提出警告,PaperCut NG與PaperCut MF系統遭到零時差漏洞攻擊,迄今該公司已發布3次緊急更新,修補CVE-2026-82078、CVE-2026-81578兩個零時差漏洞,如今傳出有人用於攻擊特定領域的用戶,藉此搜刮憑證。 資安公司Arctic Wolf於9月4日揭露漏洞利用活動,攻擊者鎖定存在上述漏洞的PaperCut伺服器,利用弱點得到…
OpenAI's rebel agent swarm died young, but its chilling logs live on
OPINION You will have heard of July's OpenAI/Hugging Face incident, where thousands of the former's AI agents conducted a mass jailbreak from a notionally secure capture-the-flag lab experiment, befor…
Peers ask why UK cyber bill leaves execs off the personal liability hook
Peers have questioned why the UK's Cyber Security and Resilience Bill does not allow regulators to penalize senior executives when an organization's failure to comply involves their consent, connivanc…
Citrix NetScaler重大漏洞遭到利用
新聞8月下旬Citrix發布NetScaler ADC與NetScaler Gateway更新,修補重大等級的身分驗證繞過漏洞CVE-2026-19490,該漏洞影響特定設定的NetScaler Gateway與AAA虛擬伺服器,CVSS v4.0嚴重性評分達9.3分,如今傳出該漏洞遭到利用的現象。 根據資安新聞網站Bleeping Computer報導,9月4日漏洞威脅情報平臺Previdian…
 Phoronix@masto.ai
·